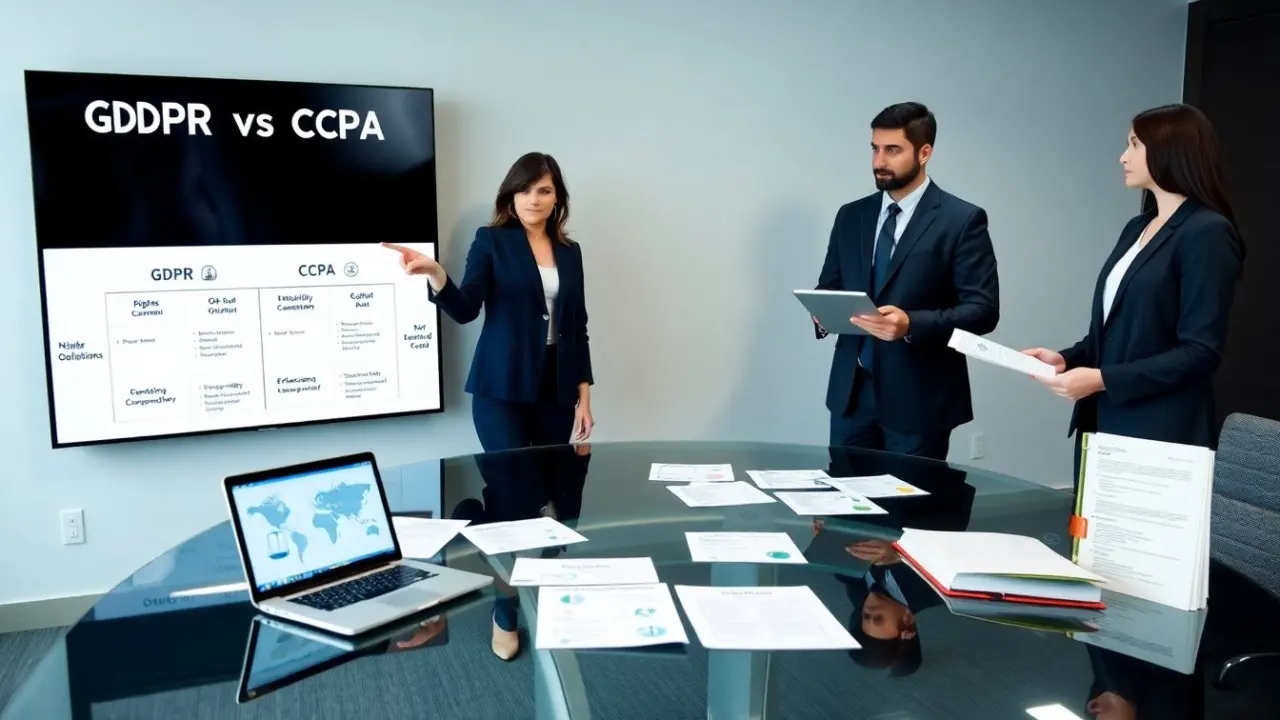
gdpr vs ccpa appears early in many compliance plans. The laws target personal data and give people rights over that data. Companies must check where they operate, what data they hold, and which law applies. This article explains who each law covers, the main differences in rights and duties, a compact compliance checklist, enforcement risks, and how to decide which rules govern data practices.
Key Takeaways
- The GDPR applies to companies processing personal data of EU residents, including those outside the EU offering services or monitoring behavior in the EU, while the CCPA applies to businesses operating in California meeting specific thresholds.
- GDPR grants rights like access, rectification, erasure, and requires lawful bases for processing, whereas CCPA gives rights to know, delete, and opt out of sale of personal information with a focus on consumer notices and non-discrimination.
- Compliance requires thorough data mapping, establishing legal bases, providing clear notices, opt-out mechanisms, updating vendor contracts, and implementing security and breach procedures.
- Noncompliance risks include heavy fines under GDPR (up to 4% of global turnover) and statutory damages under CCPA, alongside reputational and legal consequences, necessitating robust documentation and incident response.
- Companies should determine which law applies by considering where affected individuals reside, where services are offered, and how data is used, applying the strictest rules to minimize risk and adopting unified data protection controls where possible.
Who Each Law Covers And When They Apply
The GDPR covers companies that process personal data of people in the EU. It applies to controllers and processors inside the EU and extends extraterritorially to organizations outside the EU that offer goods or services to, or monitor the behavior of, people in the EU. The regulation defines personal data broadly to include identifiers, online identifiers, and anything that can be linked to an identifiable person. The CCPA covers businesses that do business in California and meet statutory thresholds related to revenue, the amount or importance of personal information processed, or the percentage of annual revenue derived from selling personal information; it applies to personal information about California residents and includes obligations for service providers acting on a business’s behalf.
Determining which law applies requires practical, documented steps: map where users and customers live, catalogue processing locations and subprocessors, review marketing and analytics activities that may target or track residents, and assess whether processing crosses the relevant jurisdictional lines. In mixed operations, both laws can apply to different datasets or activities; companies should identify overlap and treat the most protective requirements as a baseline where feasible.
Core Differences In Rights And Business Obligations
The GDPR grants a broad set of rights: access to personal data, rectification of inaccuracies, erasure (the right to be forgotten) in certain circumstances, restriction of processing, data portability to transfer data between controllers, and the right to object to processing including profiling. It also requires controllers to establish and document a lawful basis for each processing activity (such as consent, contract, legal obligation, vital interests, public task, or legitimate interests) and to implement data protection by design and by default.
By contrast, the CCPA provides California residents with rights focused on transparency and control over commercial uses of their data: the right to know what categories and specific pieces of personal information a business collects, the right to request deletion of personal information, and the right to opt out of the sale of personal information. The CCPA also includes protections against discrimination for exercising rights. Operationally, GDPR obligations tend to be process- and governance-oriented (records of processing, data protection impact assessments for high-risk operations, and, for many organizations, appointing a data protection officer), while CCPA obligations emphasize notices at collection, maintaining an opt-out mechanism (such as a web-based preference signal), and specific contractual terms for service providers and contractors.
Practical differences affect workflows: GDPR consent requirements are often more granular and record-keeping intensive; CCPA emphasizes consumer-facing disclosure and mechanisms to exercise rights. Understanding terminology differences—’personal data’ vs ‘personal information’, ‘processing’ vs ‘use or sale’—is essential when aligning policies and technical controls across both regimes.
Key Compliance Checklist For US And EU Operations
Companies should use a checklist to meet GDPR and CCPA duties. The checklist should include data mapping, legal bases, notices, opt-out mechanisms, vendor contracts, security measures, and breach procedures. Start with a comprehensive inventory: identify categories of personal data collected, sources, processing purposes, retention periods, and recipients. Link each processing activity to a legal basis for GDPR and to the lawful purpose and categories required under CCPA. Maintain records of processing activities and consents where applicable.
Privacy notices must be tailored: GDPR requires clear information on legal bases and rights, while CCPA requires disclosure of categories collected and shared, the purposes of collection, and an explicit description of the right to opt out of sales. Implement consumer request workflows that capture, verify, and respond to access, deletion, and portability requests within required timeframes; log all requests and outcomes. For data transfers across borders, document safeguards under GDPR (such as standard contractual clauses or other permitted transfer mechanisms) and ensure contractual terms with processors and service providers meet both regimes’ requirements. Conduct DPIAs for high-risk processing under GDPR and risk assessments that support CCPA compliance decisions.
– Data Mapping, Legal Bases, Notice, And Opt-Out Mechanisms
Data mapping helps the company locate personal data and track flows. The company should list data types, sources, recipients, and retention periods and flag where special categories or sensitive data are processed. For GDPR, document the lawful bases for each processing activity, maintain records of processing activities, and capture explicit consent where it is relied upon. For CCPA, provide collection and sale notices, a dedicated web page or preference signal for opt-out of sales, and a clear mechanism to handle deletion requests and rights-to-know requests.
Operationalize these elements by integrating privacy requirements into product design: build APIs and admin tools to extract user data for portability, maintain access controls and encryption for data at rest and in transit, and automate request handling where possible to meet deadlines. Train customer service and legal teams on verification standards and the documentation required to substantiate compliance actions.
Enforcement, Penalties, And Practical Risks For Companies
Supervisory authorities enforce the GDPR and can levy administrative fines and corrective measures; fines can be substantial and enforcement often includes requirements to change processing activities. The CCPA provides for state enforcement by authorities and, in certain cases, a private right of action related to data breaches that can result in statutory damages. Beyond fines and statutory damages, companies face reputational harm, remediation costs, litigation expenses, and increased regulatory scrutiny.
Practical risk management includes maintaining an audit trail of compliance activities, timely breach detection and notification procedures, and clear incident response plans that cover internal escalation, regulator notification, and consumer communication. Expect cross-border inquiries where processing spans jurisdictions and potential coordination between regulators. Regularly review guidance from supervisory authorities and updates to the law to adjust internal controls and training accordingly.
How To Decide Which Rules Govern Your Data Practices
The company should answer three questions. First, where do the affected people live? Residency and physical presence of data subjects determine whether GDPR or CCPA rights attach. Second, where does the company operate and offer services? Consider targeted marketing, localized websites, and whether your offerings are directed at residents of the EU or California. Third, what data does the company collect and how does it use that data? Determine whether you are selling personal information, engaging in profiling or behavioral advertising, or conducting high-risk processing that would trigger additional GDPR obligations.
If people in the EU are affected, the GDPR likely applies; if California residents are affected and the company meets thresholds, the CCPA likely applies. When both laws apply, map overlapping obligations and implement the most protective measures as a default. Practical steps include adopting unified privacy notices, centralizing request handling, harmonizing retention schedules, and using contract templates that address both GDPR and CCPA requirements. Consult counsel for complex cross-border operations, keep policies current as laws and guidance evolve, and document the decision process so supervisory authorities or auditors can understand how you determined applicable rules.