PII data protection must start with clear rules and practical steps. It protects individuals and reduces fines. It reduces theft and misuse. It helps organizations keep trust and meet law obligations. This guide gives focused, actionable controls and policies. It shows how teams can protect PII data protection with technical and human controls.
Key Takeaways
- Effective PII data protection starts with clear rules, practical steps, and classifying data into public, confidential, and restricted tiers to manage risk appropriately.
- Organizations must implement core technical controls like encryption, access control, monitoring, and data minimization to safeguard PII data protection.
- Strong authentication practices, including multi-factor authentication and role-based access, are essential to reduce unauthorized exposure of PII data protection assets.
- Encrypted data both at rest and in transit, combined with proper key management and regular verification, greatly enhances PII data protection.
- Clear policies, employee training, and compliance mapping help maintain consistent PII data protection and minimize human errors.
- Having an incident response plan focused on PII data protection, with breach detection, containment, communication, and regular exercises, strengthens organizational readiness and legal compliance.
Why PII Protection Matters Now: Risks, Costs, And Regulatory Pressure
Breaches expose PII data protection to theft and resale. Attackers target names, identifiers, and financial details. Companies suffer direct losses, legal fines, and reputation damage. Regulators increase fines for weak PII data protection and they audit controls more often. Consumers expect clear handling of their data and they will switch after a breach. Boards now ask for concrete PII data protection metrics. Insurers raise premiums for poor PII data protection posture. Small errors in handling can trigger major cost and legal exposure.
Types Of PII And How To Classify Sensitive Data
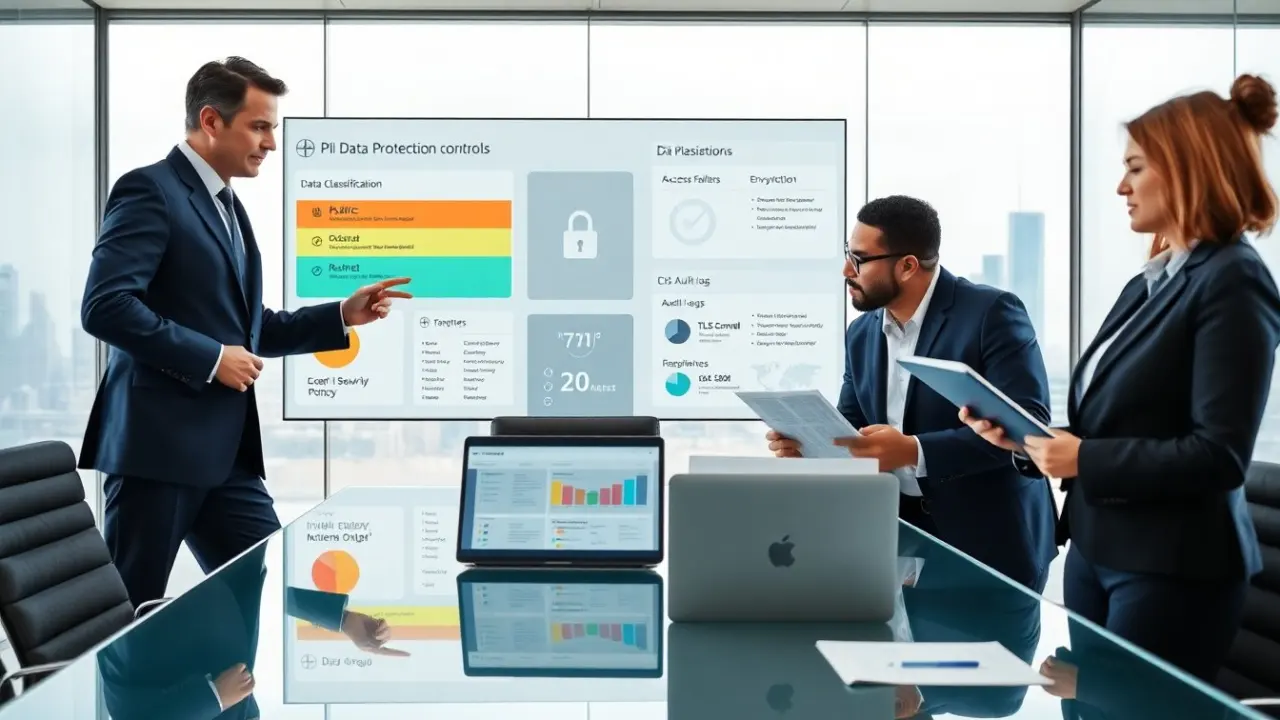
Teams must list the PII types they hold. Common PII includes names, emails, phone numbers, and national IDs. Sensitive PII includes financial records, health details, and biometric data. Classification assigns each item a risk tier and handling rule. Use three tiers: public, confidential, and restricted. Public PII has low risk and minimal controls. Confidential PII requires access controls and logging. Restricted PII needs stronger controls, encryption, and limited retention. Label data at ingestion and review labels quarterly. This approach makes PII data protection repeatable and auditable.
Core Technical Controls For PII Protection
Organizations must set baseline technical controls for PII data protection. Controls should include access control, encryption, monitoring, and data minimization. They should enforce least privilege and log all access. They should apply segmentation and controlled backups. They should remove unnecessary copies and rotate keys. They should test controls with regular scans and targeted audits. Each control should map to a policy and a metric. Teams should measure access failures, encryption coverage, and audit completion to track PII data protection progress.
Access Controls And Authentication Best Practices
Teams must enforce strong authentication for PII data protection. Use multi-factor authentication for all privileged accounts. Apply role-based access and time-limited permissions. Require unique accounts and avoid shared credentials. Use conditional access rules for high-risk locations and devices. Audit access lists quarterly and remove stale permissions. Use just-in-time access for admins and record all sessions. These steps reduce unauthorized access and limit exposure of PII data protection assets.
Encryption At Rest And In Transit: Implementation Guidance
Encrypt PII data protection items in motion and at rest. Use TLS for all network traffic that carries PII. Use full-disk encryption on laptops and encrypted storage for databases that store PII. Use field-level encryption for highly sensitive values like SSNs and payment tokens. Manage keys in a hardened key management service and rotate keys on a schedule. Apply envelope encryption when using third-party services. Verify encryption with periodic checks and document encryption coverage for audits of PII data protection controls.
Policies, Compliance, And Employee Practices For PII Safety
Clear policies help teams meet PII data protection goals. Create a data handling policy that defines roles, retention, and acceptable use. Train staff on specific steps for handling PII and test them with role-based exercises. Require data minimization at collection points and ask for consent where required. Enforce secure remote work rules and phishing defenses. Maintain a compliance register that maps laws to controls and review it when rules change. Regular training and simple checklists reduce common mistakes that harm PII data protection.
Incident Response And Breach Notification Steps Every Team Needs
Prepare an incident plan that centers on PII data protection. Detect breaches with monitoring and alerts. Contain the incident by revoking access and isolating affected systems. Preserve evidence for forensic review. Notify legal and compliance teams to assess notification obligations. Communicate clearly to affected individuals and regulators within required timelines. Document every action and update the plan after lessons learned. Run tabletop exercises twice a year to keep response teams ready and to improve PII data protection readiness.