AI regulation in the US appears in many laws and agency actions in 2026. The federal government sets standards, funds research, and issues guidance, while agencies translate broad policy goals into operational rules and enforcement priorities. States pass their own rules, sometimes filling perceived federal gaps or setting higher bars for consumer protection. Businesses must track federal rulemakings, agency guidance, and state laws — and align internal practices to meet overlapping requirements. Citizens should watch privacy, safety, and civil rights changes because regulatory choices affect how personal data is used, how automated decisions are explained, and what remedies exist when harms occur. The next sections list the main federal actions, core policy debates and high‑impact sectors, common state trends and practical effects, and a clear compliance roadmap for organizations and civic stakeholders to follow.
Key Takeaways
- AI regulation in the US involves a complex mix of federal laws, agency rules, and state laws that businesses must actively monitor for compliance.
- The federal government focuses AI regulation on safety, privacy, discrimination, transparency, and requires audits and reporting especially for high-risk sectors like healthcare and finance.
- State laws vary widely, creating a patchwork of requirements that increase compliance complexity and costs for organizations operating nationwide.
- High-risk sectors such as healthcare, finance, government, and critical infrastructure face strict documentation, testing, and oversight rules to ensure AI safety and accountability.
- Organizations should implement a clear compliance roadmap including model inventory, risk classification, testing, staff training, and continuous monitoring to meet regulatory demands.
- Civic stakeholders and legal teams play a critical role by participating in rulemakings, monitoring changes, and advocating for privacy, civil rights, and transparent impact assessments.
The Current Federal Landscape: Laws, Agencies, And Ongoing Bills
The federal government issued multiple actions on ai regulation in the us by 2026. Congress passed targeted statutes on algorithmic bias and critical system audits, and several standing agencies expanded their AI workstreams. The White House released an executive order that set safety goals and procurement rules for federal purchases, and it coordinated interagency efforts to harmonize standards where feasible. Agencies wrote rules and guidance: the Federal Trade Commission focused on deceptive or unsafe AI practices; the Department of Commerce supported infrastructure for model testing and interoperable standards; and NIST published voluntary risk-management frameworks, best practices, and technical guidance intended to be usable by both regulated entities and auditors. Sector agencies — including HHS and the FDA — provided guidance and enforcement expectations for medical AI products, while the SEC and banking regulators clarified disclosure and risk-management expectations where AI affects investors or systemic risk. Several broader bills remain in committee; they aim to establish national privacy guardrails, create clearer product‑liability pathways for harmful outputs, and set thresholds for federal oversight of high‑risk systems. Taken together, the federal mix relies on agency rulemaking, targeted statutes, executive policy, and funding for public research and testing. This combination creates both prescriptive rules in some areas and flexible, principles‑based approaches in others. For organizations, the practical implication is continuous monitoring of agency notices, rulemakings, and guidance documents as well as engagement in public comment periods; for citizens, it means paying attention to enforcement patterns and administrative interpretations that shape how broadly or narrowly obligations are applied.
Top Policy Issues And High‑Impact Sectors Shaping Regulation
Lawmakers and agencies focus on a few key policy issues for ai regulation in the us. Core themes include safety (reducing physical and systemic harms), privacy (controlling data collection and retention), nondiscrimination (preventing biased outcomes), transparency (enabling meaningful explanations and documentation), and accountability (assigning responsibility and remediation pathways). Practical regulatory tools in use or under discussion include risk‑based classification of systems, mandatory incident reporting, model documentation requirements (e.g., provenance and training data descriptions), independent testing or audits for high‑risk systems, and procurement conditions for public contracts. Policymakers are also wrestling with liability frameworks for model outputs, the appropriate regulation of platform intermediaries, and limits on biometric surveillance such as facial recognition in specific contexts. Market actors and civil society push for stronger consumer protections, explainability, and access to remedies; industry groups and tech firms emphasize standards, testing incentives, and interoperability to avoid stifling innovation. Funding for public‑sector model testing laboratories and for interpretability research increased in 2026, creating new public resources for validation and benchmarking. Courts and enforcement agencies have begun to shape the practical reach of these rules through case law and penalty decisions; those precedents will influence how aggressively regulators impose obligations and how companies structure compliance programs. Below are concrete sector considerations where regulatory pressure is concentrated.
Sector Examples: Healthcare, Finance, Government, And Critical Infrastructure
Healthcare systems use AI for diagnosis, triage, and workflow optimization; regulators require clinical validation, defined performance metrics, post‑market surveillance, and transparent labeling about intended use. In practice, this means model developers and hospitals must document training data limitations, monitor for performance drift, and implement clinician oversight. Financial institutions use AI for credit decisions, fraud detection, and automated trading; regulators expect processes to prevent discriminatory lending outcomes, to detect market‑manipulative behavior, and to disclose material AI‑driven decision processes to supervisors and, in some cases, to consumers. Government agencies employ AI in eligibility determinations, immigration screening, and public‑safety analytics; transparency, impact assessments, and procedural safeguards are increasingly required to protect due process and civil rights. Critical infrastructure operators — utilities, transportation networks, and water systems — integrate AI into control and monitoring systems; regulators focus on resilience, fail‑safe design, and supply‑chain security for models used in operational contexts. Across these sectors, common regulatory expectations include comprehensive documentation (model cards, data sheets), independent or internal audits, human‑in‑the‑loop processes for high‑consequence decisions, incident reporting, and remediation plans. For organizations this typically translates into cross‑functional compliance teams, enhanced testing regimes, stronger vendor governance, and more formalized escalation paths when anomalies or harms are detected. For affected communities, the changes mean clearer routes to raise concerns and greater visibility into how automated systems affect access to services and rights.
State-Level Patchwork: Major State Laws, Preemption Risks, And Practical Effects
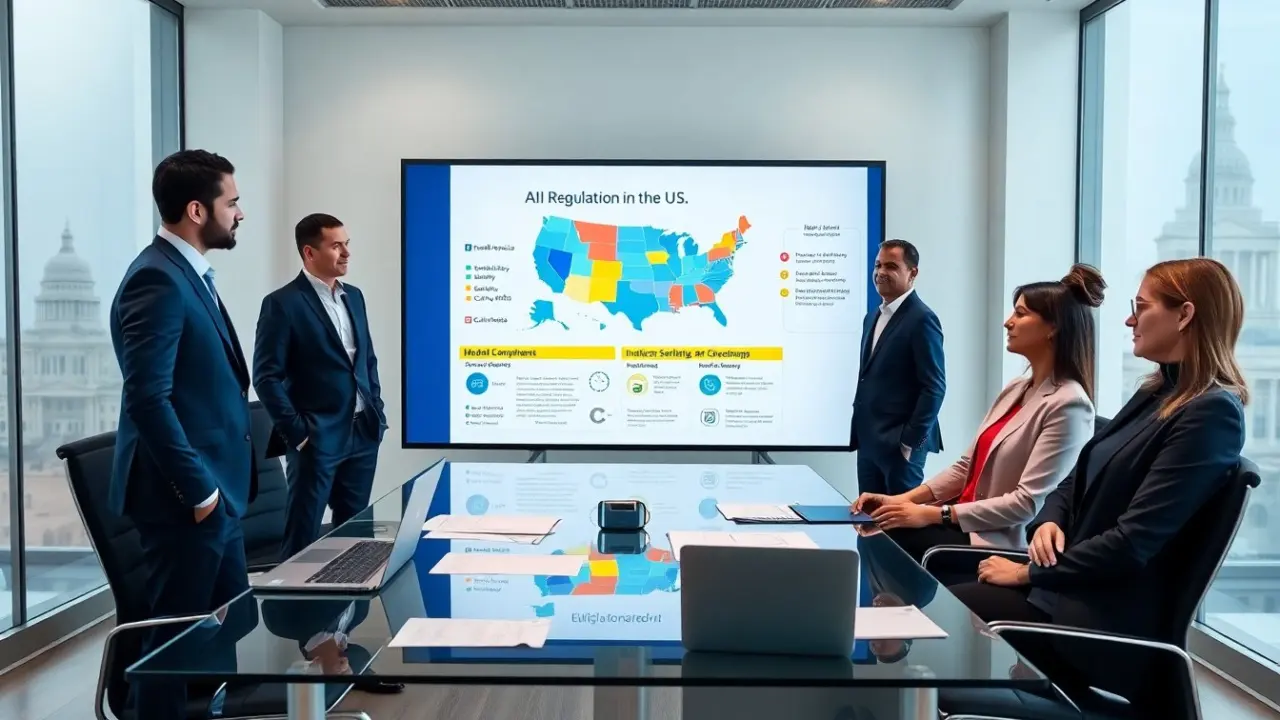
States passed many laws on ai regulation in the us by 2026, producing a varied landscape that often reflects local policy priorities. California strengthened privacy protections and expanded algorithmic fairness requirements for public agencies and certain private actors. New York and Illinois updated biometric and consumer protection laws that affect how companies collect and process face and voice data. Several states require algorithmic impact assessments or public reporting for government use, while other states have imposed sector‑specific bans or restrictions on surveillance technologies. This patchwork creates compliance complexity: companies operating across states may need multiple disclosure regimes, consent workflows, and retention schedules. The federal government has periodically considered preemption as a way to create more uniform national rules; proponents argue preemption reduces regulatory compliance costs, while opponents warn it could lower protections in states that seek stronger safeguards. Currently, the absence of full federal preemption means organizations must map state requirements to federal rules carefully, update policies, negotiate contract clauses with vendors, and implement geo‑specific controls where necessary. Practical effects seen in the field include higher compliance and legal costs, centralization of data governance functions, constrained product features in stricter jurisdictions, and strategic decisions to limit or phase deployments in states with particularly stringent rules. For civil‑society groups and state policymakers, the dynamic also creates opportunities to pilot stronger oversight regimes and to surface best practices that might inform federal standardization over time.
A Practical Compliance Roadmap For Organizations And Civic Stakeholders
Organizations should build a clear plan to comply with ai regulation in the us that treats legal, technical, and operational requirements as integrated. First, inventory models and associated datasets, capturing provenance, intended use, and known limitations. Second, classify systems by risk level and applicable sector rules so that high‑risk systems trigger heightened controls. Third, apply testing, documentation, and monitoring to high‑risk systems: establish validation tests, maintain model cards and data sheets, and set thresholds for model‑retraining or withdrawal. Fourth, assign a compliance lead and governance structure that includes legal, privacy, security, and product teams; define incident response steps, reporting chains, and remediation timelines. Fifth, update procurement clauses and vendor‑management practices to require appropriate audit rights, transparency obligations, and liability allocations. Sixth, train staff across functions on bias testing, data handling, and incident escalation; include tabletop exercises that simulate regulatory audits or incident reporting. Civic stakeholders should press for transparent impact assessments, public audits, and accessible complaint mechanisms; they should participate in public comment periods and support litigation or advocacy where necessary to enforce standards. Legal teams should actively monitor federal rulemakings, state laws, and key court decisions and translate them into operational controls. Tech teams should adopt reproducible development practices: version control, robust test suites, model cards, and rollback plans. Policy teams should track bills that would change liability, disclosure, or preemption rules and coordinate with industry associations where appropriate. Public interest groups should focus on privacy, civil rights, and access to remedies. Together, these steps reduce legal and operational risk, improve public trust, and create more resilient systems that can detect and address harms early while enabling continued innovation within the evolving framework of ai regulation in the us.